



Direct Answer
Initial passwords are risky during onboarding because they're often assigned according to a predictable pattern and handed over insecurely – read aloud, sent over chat, or handed over on a sticky note. With pre-provisioning, devices, accounts, and credentials are created automatically before the first working day and delivered through a private channel. The manual handover moment disappears entirely. No one reads a password aloud, types it into a chat, or hands it over in person, and employees set their own password at first login.
Key Takeaways
- Initial passwords are a classic weak point: first-time passwords are often assigned according to a predictable pattern, such as a combination of name and start date, or as a single standard password for all new employees.
- GDPR demands more than "just any" password: authentication by password is a technical and organizational measure under Art. 32 GDPR, and inadequate implementation can trigger fines.
- Pre-provisioning removes the risky handover moment: accounts and credentials are generated automatically before the first working day and delivered via an automated welcome email to a private address. No one reads or sends the password manually.
- deeploi automates the process: as soon as new employees are added in an HRIS tool, deeploi configures the device, accounts, and security policies in 3 to 5 minutes, with no manual password handover at all. HR managers save recurring effort per onboarding, and employees start off with a securely configured account from their very first login.
What is an initial password, and why is it risky during onboarding?
An initial password is the temporary first password assigned when a new user account is created, meant for the first login and then, in theory, changed afterward. In practice, virtually every new employee receives such an initial password at the start, but its confidentiality is only inadequately organized at many companies.
First-time passwords are often created according to a predictable pattern, such as a combination of name and start date, or even the same standard password is used for all new employees.
Why is that dangerous? Anyone who knows the pattern – including former employees – can potentially gain access, and the longer an initial password stays unchanged, the larger the window for misuse.
On top of that comes the delivery problem: the process of handing over the first password is considered one of the biggest weak points in the entire password lifecycle. If the password is sent in plain text by email or chat during that process, it remains vulnerable in transit. The sticky note on the monitor isn't an exaggeration – it's lived practice at many small companies.
CTA: Onboarding without initial password risk
No more insecurely transmitted initial passwords, no more waiting on IT on the first working day: deeploi sets up devices, accounts, and security policies automatically, triggered directly from your HR system, so new employees are ready to go from day one.
CTA Button: Automate onboarding now → https://www.deeploi.io/en/book-your-demo
The legal side: initial passwords and GDPR
Authentication via username and password counts as a technical and organizational measure (TOM) under Art. 32 of the GDPR. That applies explicitly to initial passwords too, not just to passwords employees later choose themselves. Anyone who creates new accounts with a weak or insecurely transmitted first password may not be meeting this requirement adequately.
The consequence is more than theoretical: if controllers implement inadequate technical and organizational measures, fines can be imposed under Art. 83(4) GDPR. For companies without their own IT team, that's an unpleasant surprise, because no one deliberately plans an insecure onboarding process. It usually arises from time pressure and a lack of coordination between HR and IT.
deeploi, as an All-in-One IT Management Platform, is ISO 27001 certified – the internationally recognized standard for information security management – and GDPR compliant.
Three patterns that make initial passwords a risk
Three recurring patterns turn a simple first password into a genuine security risk.
Just how real the threat behind this is becomes clear from current figures: in the Verizon 2025 Data Breach Investigations Report, system intrusion attacks in the EMEA region nearly doubled to 53% within a single year, and nearly a third (29%) of all breaches in the region originated internally – some through unintentional error rather than malicious intent. Every poorly structured or insecurely transmitted initial password adds directly to that internal attack surface.
Pre-provisioning vs. a password reset portal
Pre-provisioning means: devices and accounts are fully set up and equipped with security policies before new employees use them for the first time, including access to Microsoft 365 or Google Workspace.
The account and an automatically generated password are created before the start date, during a lead time that IT managers define themselves.
Credentials reach new employees via an automated welcome email sent to their private email address, typically around three days before their first working day – with no person ever reading the password aloud, typing it into a chat, or handing it over in person.
At first login, new employees set their own, new password directly. From that moment on, only they know the password actually in use.
A self-service portal only solves half the problem. Employees reset their initial password themselves there, usually on their first working day. The risky handover moment is defused, but it remains part of the process, because someone still has to communicate how the first login works. Pre-provisioning moves this step entirely ahead of the first working day and automates it, so no manual handover moment remains at all.
This is further secured through multi-factor authentication (MFA) and, increasingly, passkeys – a passwordless login method that can't be stolen, lost, or guessed. Passkeys are also more resistant to phishing, because they don't work on fake login pages.
Passwords don't disappear entirely, though. For services without SSO or MFA, strong, individual passwords and a password manager remain sensible – otherwise, many people end up reusing the same password across multiple services.
How deeploi automates pre-provisioning for companies with and without an IT team
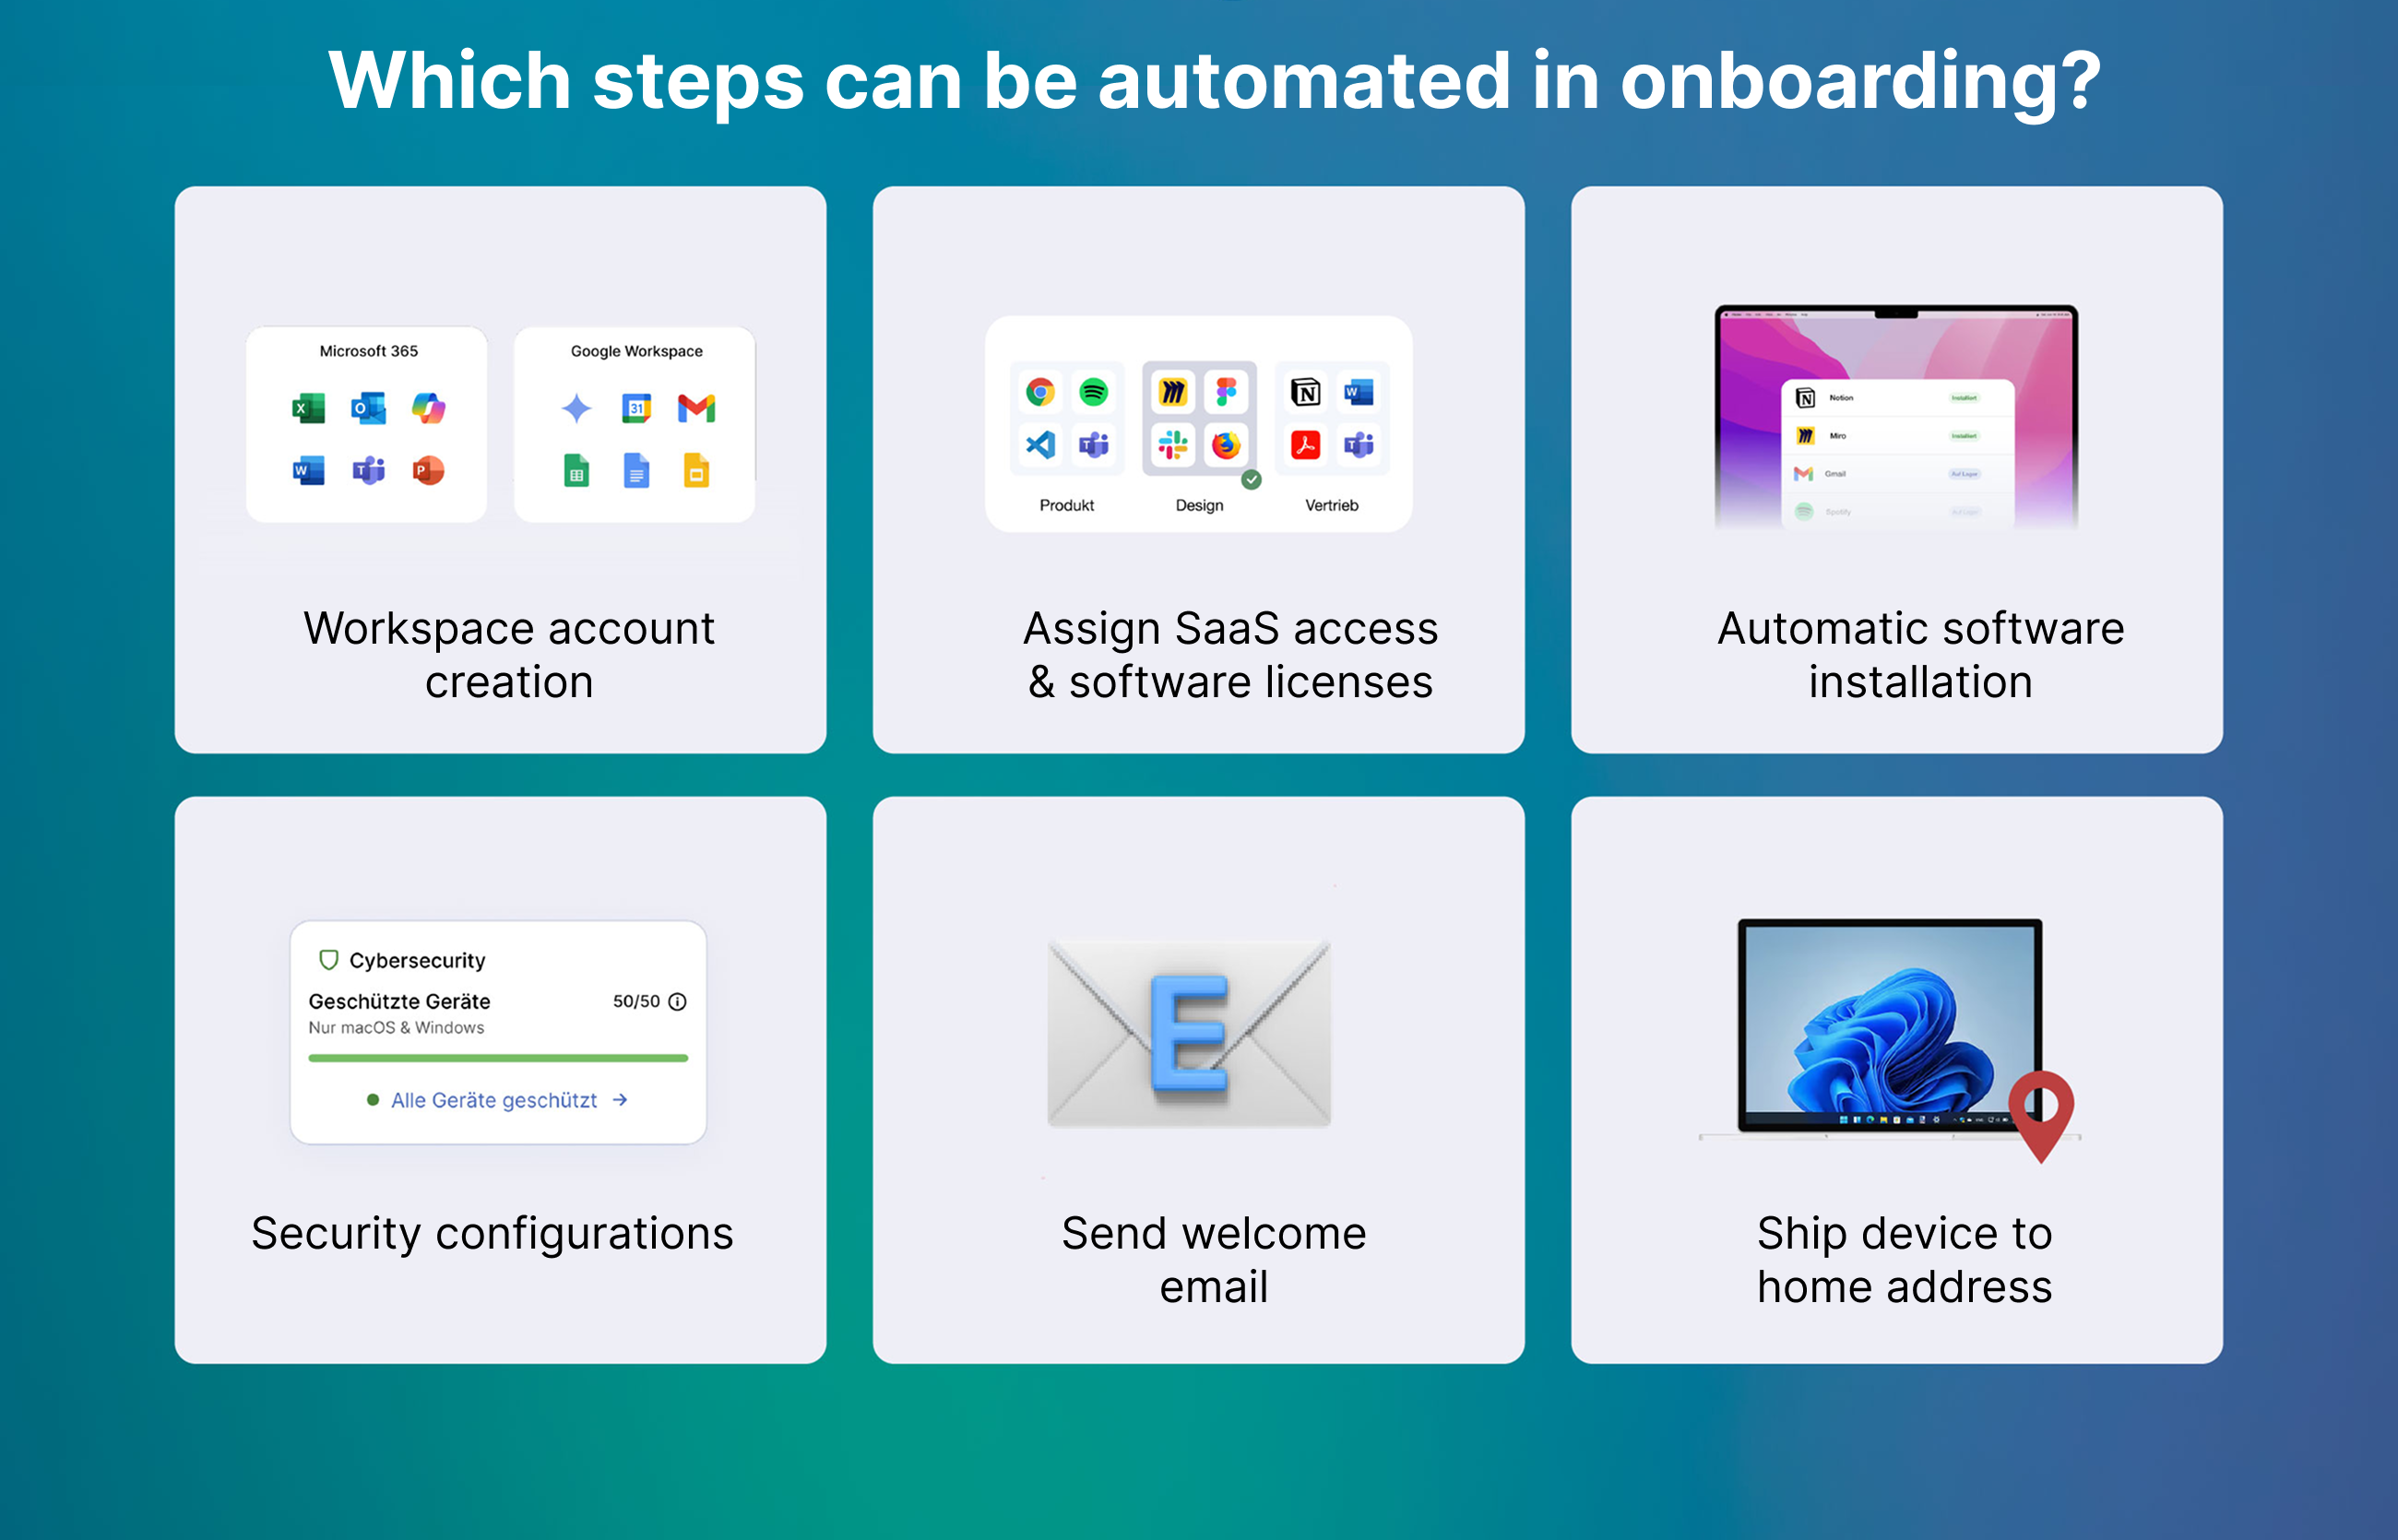
deeploi is an All-in-One IT Management Platform that takes over exactly this process. deeploi connects with Personio, Factorial HR, BambooHR, and other HRIS tools. As soon as a new personnel record is created, it automatically triggers the entire IT provisioning – device, accounts, software packages, and security policies included.
Setup takes 3–5 minutes instead of the usual 2–3 hours of manual work, with up to 95% less manual IT effort overall.
200+ companies already rely on this automated workflow.
24 to 48 hours, depending on the order, is how long it takes for a device to be configured and ready to use.
Up to 95% less manual IT effort overall compared with traditional setup.
Good to know: if a question does come up after setup, deeploi's IT support team is on hand, responding in German and English within an average of 12 minutes (SLA: 30 minutes). For simple requests, Sam, deeploi's AI agent, is available around the clock and hands off seamlessly to the human expert team for more complex issues.
✔ For companies without their own IT team, this means: security is part of the process from the very first minute, without HR managers having to become IT experts themselves.
✔ For companies with an existing, small IT team, the effect looks different: routine tasks like device setup and account provisioning run automatically in the background, freeing the team to focus on more complex projects instead of getting bogged down in recurring onboarding busywork.
How pre-provisioning works at deeploi, step by step
At deeploi, the process looks like this in detail:
The trigger is a single entry in the HR system: the new employee's start date and role.
Full provisioning then follows automatically, with no manual ticket and no improvised password assignment by whoever happens to have time.
On the device side, this runs through zero-touch provisioning: the device is enrolled in mobile device management (MDM) and sets itself up with apps, security policies, and accounts – with no manual intervention at all.
The level of automation currently differs by device type at deeploi:
This automation applies to the device side only. On the account side, the process is the same regardless of operating system: role-based software packages and access are set up in advance, and the workflow for the Microsoft 365 or Google Workspace account is identical for deeploi across both operating systems. The account and password are generated automatically and delivered via welcome email.
Even with a late or incomplete HR entry, the process at deeploi stays reliable:
- Daily sync: the HR system is reconciled once a day.
- Manual setup possible: for freelancers, temporary employees, or cases the HR system misses.
- Early notification: IT managers are notified around one month before the start date.
- Flexible timing: account creation runs two weeks before the start date by default, or immediately for later notifications.
- Fallback for errors: if automated setup fails – for example, due to a missing license – the case is flagged and taken over manually by a deeploi IT expert. The next daily sync run recognizes the account that's already been created and doesn't set it up twice.
Crucially: the password is still generated automatically in every one of these cases – a late setup only changes the timing, never the delivery method.
The result: the new employee turns on the device, logs into an already configured account, and gets to work. No one types, speaks, or hands on a password – it's created and changed automatically, long before the first working day even begins.
Conclusion: security starts before the first login
The insecure, manual handover moment is the real risk factor – more so than the initial password itself. Pre-provisioning shifts security from "hopefully no one does it wrong" to "it can't be done wrong," because accounts and credentials are created and delivered automatically, long before the first login ever takes place. For companies that want to automate this step, deeploi takes over the complete IT provisioning for onboarding, triggered directly from the HR system and with no manual password handover.
Onboarding without initial password risk
No more insecurely transmitted initial passwords, no more waiting on IT on the first working day: deeploi sets up devices, accounts, and security policies automatically, triggered directly from your HR system, so new employees are ready to go from day one.
{{cta}}
Frequently asked questions
Why are initial passwords especially risky for companies without their own IT team?
Without dedicated IT review, no one usually notices when first-time passwords are assigned according to a predictable pattern or sent insecurely by email or chat. HR managers often handle the technical setup on the side, with no one routinely double-checking the steps, which lets exactly these patterns go undetected for long periods.
How can you onboard employees without handing over an initial password, if you don't have an IT team?
Through an automated all-in-one platform like deeploi, which sets up devices and accounts in advance, triggered by the HR system, and delivers credentials automatically via welcome email. No internal IT expertise is needed, because configuration, access rights, and multi-factor authentication run automatically in the background instead of being assigned manually step by step.
What's the difference between pre-provisioning and a self-service portal for initial passwords?
A self-service portal makes the handover safer, because employees reset their own initial password themselves, usually on their first working day. Pre-provisioning starts earlier: the account and password are created automatically before the start date and delivered via welcome email to a private address, so the manual handover moment disappears entirely and employees set their own, final password directly at first login.
Do companies with an existing IT team also benefit from pre-provisioning?
Yes. Even with an existing IT team, routine tasks like device setup and account provisioning disappear for every new hire. The team can focus on strategic, more complex IT projects instead of manually working through recurring onboarding busywork.